Build and test. Seven of the eight tools compared here document build coverage, and six document test, four touch security, and one covers deploy and operate. Maturity tracks verification cost: an agent can run a test suite and check its own work, which is much harder at the deploy stage.
8 Best AI SDLC Tools in 2026
Explore 8 AI SDLC tools mapped to the lifecycle stage each one covers, with integration notes and guidance on choosing between point tools and platforms.


Executive Summary
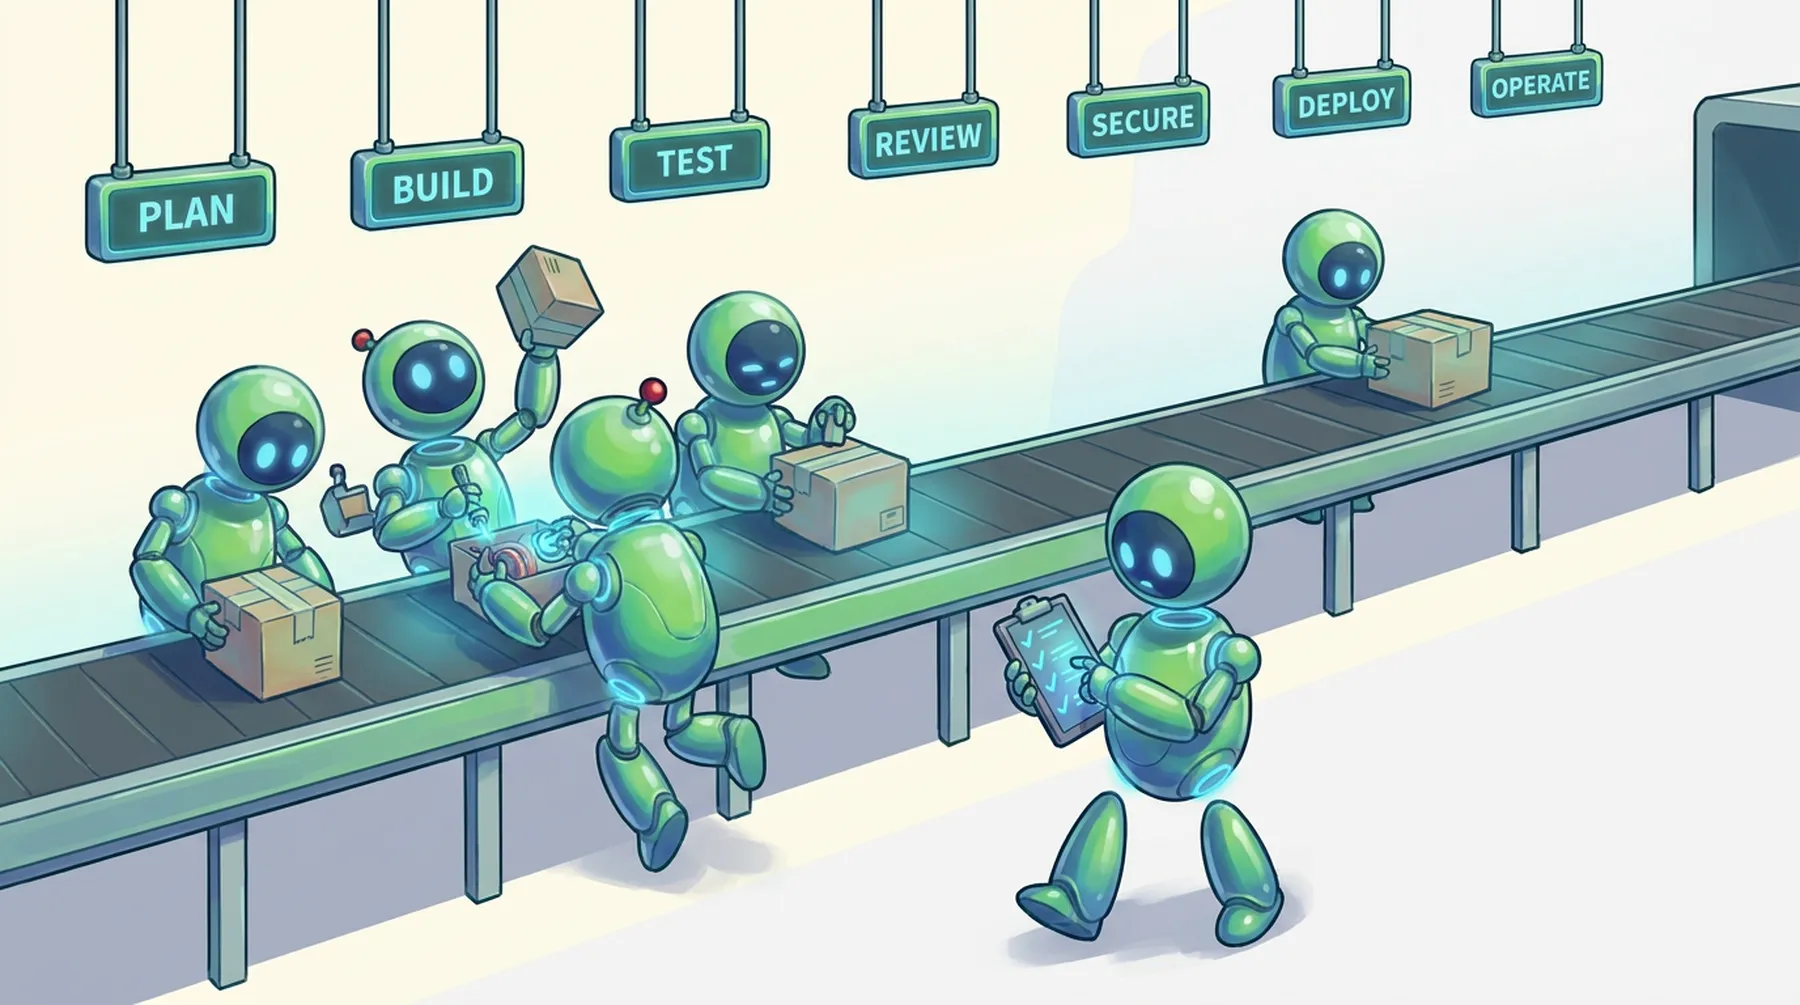
Most AI SDLC tool shortlists get built backward. A team picks the tool with the best demo, then finds it covers one stage of a lifecycle that has seven. This comparison runs the other way: each of the eight tools below sits at the stage its own documentation says it covers, with the source next to the claim.
It is written for platform engineering leads and engineering managers who already run a toolchain and are deciding what to add. Nothing is ranked or scored. Every entry rests on vendor documentation re-checked on 15 September 2026, not on benchmarking.
Key takeaways
AI SDLC tools cover individual lifecycle stages rather than the full lifecycle, so a shortlist should start with a named stage gap.
Kiro spans structured planning through implementation and testing, Codex and Cursor cover build, Devin covers migrations and review, Snyk covers security fixes, and Harness covers CI/CD.
Coverage spans eight tool clusters across build and test, and only one documents anything at the deploy or operate stage.
Integration surface decides adoption: a tool attaches inside the git host, the IDE and CLI, the pipeline, or an API.
Point solutions offer stronger capability at one stage, and platforms offer one control surface with a weaker fit at each stage.
BAND records which agent took which piece of work and whether the handoff finished, regardless of the tools each stage uses.
How We Evaluated the Best AI SDLC Tools
Four criteria decided what made the list.
Documented stage coverage. The vendor publishes what the tool does at a named lifecycle stage. Marketing claims did not count.
Integration with an existing toolchain. The reader already owns a git host, a pipeline, and an IDE. A tool that expects a clean slate is a migration, not an addition.
Controls and governance. Whether the vendor documents identity, permissions, policy, or audit around the agent's work.
Deployment model at scale. Whether an admin can enable, restrict, or turn off the tool for a whole organization.
The honest part: this rests on published documentation rather than benchmarking, and no entry is ranked above another. Two of the eight documentation URLs had already moved by 15 September 2026, so every capability sentence cites its page at the claim.
8 Best AI SDLC Tools in 2026
The eight run in lifecycle order, from planning to CI/CD, rather than by preference. If you are scanning for the best AI tools for SDLC work at one stage, read the Best for line and skip the rest.
1. Kiro
Best for: teams whose gap is planning, before an agent writes code.
Kiro's specs produce requirements.md, design.md, and tasks.md through a three-phase workflow that runs in the IDE, the CLI, and the web. Requirements use EARS notation, and independent tasks execute concurrently in dependency waves.
Not covered: review, security, deployment, and operations.
2. GitHub Copilot cloud agent
Best for: build work that starts and ends inside GitHub.
It researches a repository, plans, changes code on a branch, and opens a pull request from an ephemeral environment powered by GitHub Actions. Start it from the agents panel, a GitHub issue, an IDE, or by assigning a security alert from a security campaign.
Not covered: repositories hosted elsewhere. One task means one branch and one pull request, and sessions stop after 59 minutes.
3. OpenAI Codex cloud
Best for: several build tasks at once, off the developer's machine.
Codex checks the repository into a container, runs your setup script, then edits and verifies in a loop, reading lint and test commands from AGENTS.md (cloud environments). Work starts in the web app, GitHub, GitLab, Linear, or Slack, and /review starts a dedicated reviewer in the app, CLI, and IDE extension that reports prioritized findings without changing the working tree.
Not covered: planning. Agent-phase internet access is off by default and secrets are stripped before that phase begins.
4. Cursor Cloud Agents
Best for: build tasks that need a real machine, including work crossing repositories.
Each agent gets its own virtual machine with the repository, dependencies, secrets, and network access, so it can build, run tests, and drive a browser against the result. Multi-repo environments let one agent change frontend, backend, and infrastructure repositories in a single run.
Not covered: deployment and production operations as dedicated lifecycle stages.
5. Devin
Best for: migrations, framework upgrades, and backlog work nobody schedules.
Cognition documents language migrations, framework upgrades, pull-request review, and unit test writing as Devin's strengths. Its subagents share tools and codebase context with the parent but not its conversation history, and cannot spawn children unless a custom profile raises the nesting limit.
Not covered: deployment, and what happens to the change after merge.
6. CodeRabbit
Best for: review capacity when agents open more pull requests than people read.
CodeRabbit reviews pull requests and also runs in the IDE and the CLI, with Triage to rank a queue by value and risk and Change Stack to read a large diff as logical cohorts (CodeRabbit docs). From a Slack or Discord thread, its agent investigates the codebase, generates an implementation plan, and opens a pull request.
Not covered: test authoring, deployment, and operations.
7. Snyk Agent Fix
Best for: closing the findings Snyk Code already produces.
Agent Fix generates candidates against a database of more than 35,000 expert-written fix pairs, rescans each one, and feeds a failed scan's error back into the model for a corrected attempt. It covers every language Snyk Code supports, and Snyk states it does not train on customer code.
Not covered: vulnerabilities spanning several files. Fixes are single-file, and the docs require human review.
8. Harness AI DevOps Agent
Best for: teams whose gap is the pipeline rather than the code.
The agent creates and edits steps, stages, and pipelines from natural-language prompts, generates OPA Rego policy, and works across CI, CD, IaCM, IDP, SCS, STO, DB DevOps, and Chaos Engineering. It also answers GitOps health questions, streams pod logs, and restarts deployments.
Not covered: application code. The agent runs only in the Harness UI.
Worth naming but not profiling: Qodo runs multi-agent pull-request review across the full repository rather than the diff alone.
Which SDLC Stages Does Each Tool Cover?
Stage coverage, marked only where the vendor's own documentation supports it.
Tool | Plan | Build | Test | Review | Secure | Deploy | Operate |
|---|---|---|---|---|---|---|---|
Kiro | Yes | Yes | Yes | No | No | No | No |
GitHub Copilot cloud agent | Yes | Yes | Yes | No | Yes | No | No |
OpenAI Codex cloud | No | Yes | Yes | Yes | No | No | No |
Cursor Cloud Agents | No | Yes | Yes | No | No | No | No |
Devin | No | Yes | Yes | Yes | No | No | No |
CodeRabbit | Yes | Yes | No | Yes | Yes | No | No |
Snyk Agent Fix | No | No | No | No | Yes | No | No |
Harness AI DevOps Agent | No | Yes | Yes | No | Yes | Yes | Yes |
Harness earns its build, test, secure, and deploy marks by generating the pipeline stages that run those steps, not by writing application code.
The distribution is the useful part. Seven of the eight document build coverage and six document test, four touch security, three do review, and exactly one documents anything at deploy or operate. AI tools for SDLC automation concentrate where a diff gets produced and thin out wherever the change has to survive afterward. If day-two coverage is your gap, our guide to AI agent observability tools is a better starting point than anything here.
AI SDLC Tools for CI/CD and Existing Developer Toolchains
Capability gets the demo. Integration surface decides whether the tool survives the quarter. AI SDLC tools with CI/CD integration attach in one of four places, and where a tool attaches tells you whose habits have to change.
Inside the git host. Copilot's cloud agent works only on GitHub-hosted repositories and produces one branch and one pull request per task. Nothing else moves.
Inside the IDE and CLI. CodeRabbit reviews in the editor, from the command line, and on the pull request. Snyk Agent Fix surfaces through the Snyk plugins for VS Code, Visual Studio, Eclipse, and JetBrains.
Inside the pipeline. Harness is the only entry that writes CI and CD configuration rather than consuming it, and it generates OPA Rego policy alongside the stages.
Through an API or chat surface. Cursor starts agents from Slack, Linear, a git host comment, or its API. Codex starts from GitHub, GitLab, Linear, or Slack, and CodeRabbit's agent starts from Slack or Discord.
Tools that attach to the git host need almost no toolchain work and give you almost no control over how the work runs. Tools that attach in the pipeline need real configuration and hand back policy, audit trail, and failure analysis. Run the bake-off against the toolchain you already own.
AI SDLC Tools for Large Engineering Organizations
At small scale, the question is whether the tool works. At scale, it is who can turn it on, what it can reach, and what it leaves behind. The top AI-powered SDLC tools for large organizations answer those three unevenly.
Control | What at least one vendor documents |
|---|---|
Admin enablement | Copilot Business and Enterprise need an admin policy; repository owners can opt out. Harness enables at account level with optional overrides. |
Identity and access | Cursor verifies a viewer's repository access before showing a teammate's run. Harness requires RBAC permissions for pipelines, resources, and policies. |
Data boundaries | Codex removes secrets before the agent phase and proxies outbound traffic. Snyk states customer code is not used for training. |
Capability limits | A Devin admin can pin the default subagent model or set it to None, disabling subagents entirely. |
Audit and metrics | Harness exposes a pipeline change audit trail. GitHub exposes pull request lifecycle metrics for agent-created pull requests. |
Read that as a menu, not a baseline. No single entry documents all five, and a control one vendor ships by default is a paid tier or a missing feature elsewhere. Verify each row against your own plan before it reaches procurement, because none of it is inferable from a pricing page.
Comparing AI SDLC Tools: Capabilities, Integration & Governance
Capability clusters where verification is cheap. Build and test are where an agent can check its own work: run the suite, read the failure, retry. Snyk's rescan loop and Codex's check-and-iterate loop are the same idea at different stages. Deploy and operate stay thin because a wrong answer there is expensive and slow to detect, so the one tool covering them generates configuration a human approves rather than acting directly.
Integration divides the field more sharply than capability does. Four of the eight are coding agents that differ mainly in where they run and what they can reach. Compare them on capability, and you get a tie. Compare them on integration surface, and you get a decision.
Governance is the least consistent of the three. Each vendor governs work inside its own product: Harness through RBAC and policy, GitHub through org policy and rulesets, Devin through an admin setting on subagents. None governs the work once it crosses into the next tool, because none can see it. That boundary is the subject of our guide to AI agent governance platforms.
Choosing Between Point Solutions and End-to-End AI SDLC Platforms
Point solutions win on capability at the stage you care about. Snyk Agent Fix closes a Snyk Code finding better than a general agent will, because it retries against the scanner that raised it. Your team already knows the tools, adoption cost is low, and you can remove one without unpicking the others.
Platforms win on control surface: one place to enable, one permission model, one audit trail, one invoice. The cost is a weaker fit at individual stages and a harder exit, and that gap is real. A platform's review stage rarely matches a dedicated reviewer.
The rule is short. Buy a point solution when the gap is one stage, and you can name it. Buy a platform when nobody can say what happened across stages. SDLC tools for AI-native teams usually end up as several point solutions, because the per-stage gap is the one teams can actually name.
That choice carries a cost worth stating plainly. Run a planning tool, three build agents, a reviewer, and a security fixer, and each holds its own record of the work. Nothing records which agent took which piece, whether the next one accepted it, or where the chain stopped. You find out at merge, or later.
Where BAND Fits in the AI SDLC Toolchain
Start with what BAND is not. BAND is not one of the eight and does not belong on the list. It does not plan, write, test, review, or deploy code, and it does not replace the repository, the pull-request system, or CI. Every tool above stays where it is.
BAND handles the coordination cost the previous section described. When agents from several vendors work on the same change, teams need a single account of their interactions. BAND keeps that account underneath whichever tools each stage uses.
A shared record. Text, tool calls, tool results, thoughts, and errors are recorded per room and retrievable as history, so a change's trail doesn't live across six consoles (chat rooms and routing).
Handoffs with a state. Every message carries a per-recipient status through delivered -> processing -> processed/failed, with attempt history behind it. A handoff completes when the receiver says so, not when the sender fires.
Agents from different vendors in one room. BAND's framework adapters cover LangGraph, CrewAI, Claude Agent SDK, and OpenCode, plus named adapters for two tools on this list through the GitHub Copilot and Codex integrations.
A rule for who acts. Agents process a message only when @mentioned, so a seventh agent in the room does not mean seven agents acting on one change.
Identity that survives the handoff. Each agent has a persistent handle, an owner, and organization-level visibility, which makes delegation reviewable afterward.
The limits matter as much as the mechanisms. BAND is not an LLM evaluation suite and not a model drift monitor; that layer belongs to tools like LangSmith and Arize. Cursor and Devin have no BAND adapter today, so work in those tools reaches BAND only when another agent brings the result into a room.
Pick your point solutions on documented stage coverage and integration surface, then decide separately who holds the record of what the agents did. The BAND platform is built for that second job. If you run more than two of these eight against the same repository, book a demo and bring your stage map.
Frequently Asked Questions About AI SDLC Tools
No. They add volume to the pipeline rather than bypassing it. GitHub's cloud agent runs its work inside GitHub Actions and still opens a normal pull request. Harness goes the other way and generates the pipeline stages themselves, which is CI/CD configuration, not a replacement.
Yes, and most teams end up doing it, since Copilot, Codex, Cursor, and Devin each attach in different places. The hard part is not running them. It is knowing which agent took which piece of work, whether the next one picked it up, and where a chain stopped quietly.
The controls are documented, and they differ. Codex runs each task in an isolated container with agent-phase internet access off by default and secrets removed before that phase starts. Cursor gives each agent its own virtual machine and lets admins restrict outbound domains. Read the vendor page, not the category.
Pricing here follows three shapes: per seat, per run, and consumption on tokens or compute. Copilot's cloud agent draws on GitHub Actions minutes and AI credits, and Cursor's cloud agents bill at API pricing for the selected model. Check the live pricing page before budgeting.
Sign Up For The Band
A short and to the point summary of what we've been up to, delivered once a month to your inbox.
By submitting this form, I agree to be contacted by Band and receive occasional offers & product updates via phone or email, in line with Band’s Privacy Policy.
Coding agents
What is agentic coding? How the agent loop works
Learn what agentic coding is, how the plan, act, and verify loop closes, and what separates it from the AI code completion your team already uses.
Coding agents
Agentic Coding Workflows: How AI Agents Work Together
An agentic coding workflow moves one ticket through intake, plan, implement, verify, and review. Here are the stages, the handoffs, and where a person decides.
Coding agents
Agentic Coding Best Practices for Multi-Agent Development
Four agentic coding best practices for teams running several agents: scoped ownership, context that survives handoffs, safe parallel runs, and review gates.